Evergreen specialist guide
Access management in home care: security, roles and logging
How home-care services can establish role-based access, secure onboarding and logging for digital keys.
Establish a role model
Distinguish between organisation owner, local administrator, service manager, installer, support and end user. Each role should be able to carry out necessary tasks, but no more.
Use groups
Access groups can be organised by zone, team, shift, service or geography. Groups must have a clear owner and purpose. Obsolete groups should be archived.
Time-limit temporary needs
Temporary staff, students and vendors often need access for a specific period. Automatic expiry reduces obsolete permissions.
Onboarding and offboarding
Check identity, role, device and training before activation. Remove previous permissions when a role changes. Block the account, device and medium promptly when access ends.
What should be logged?
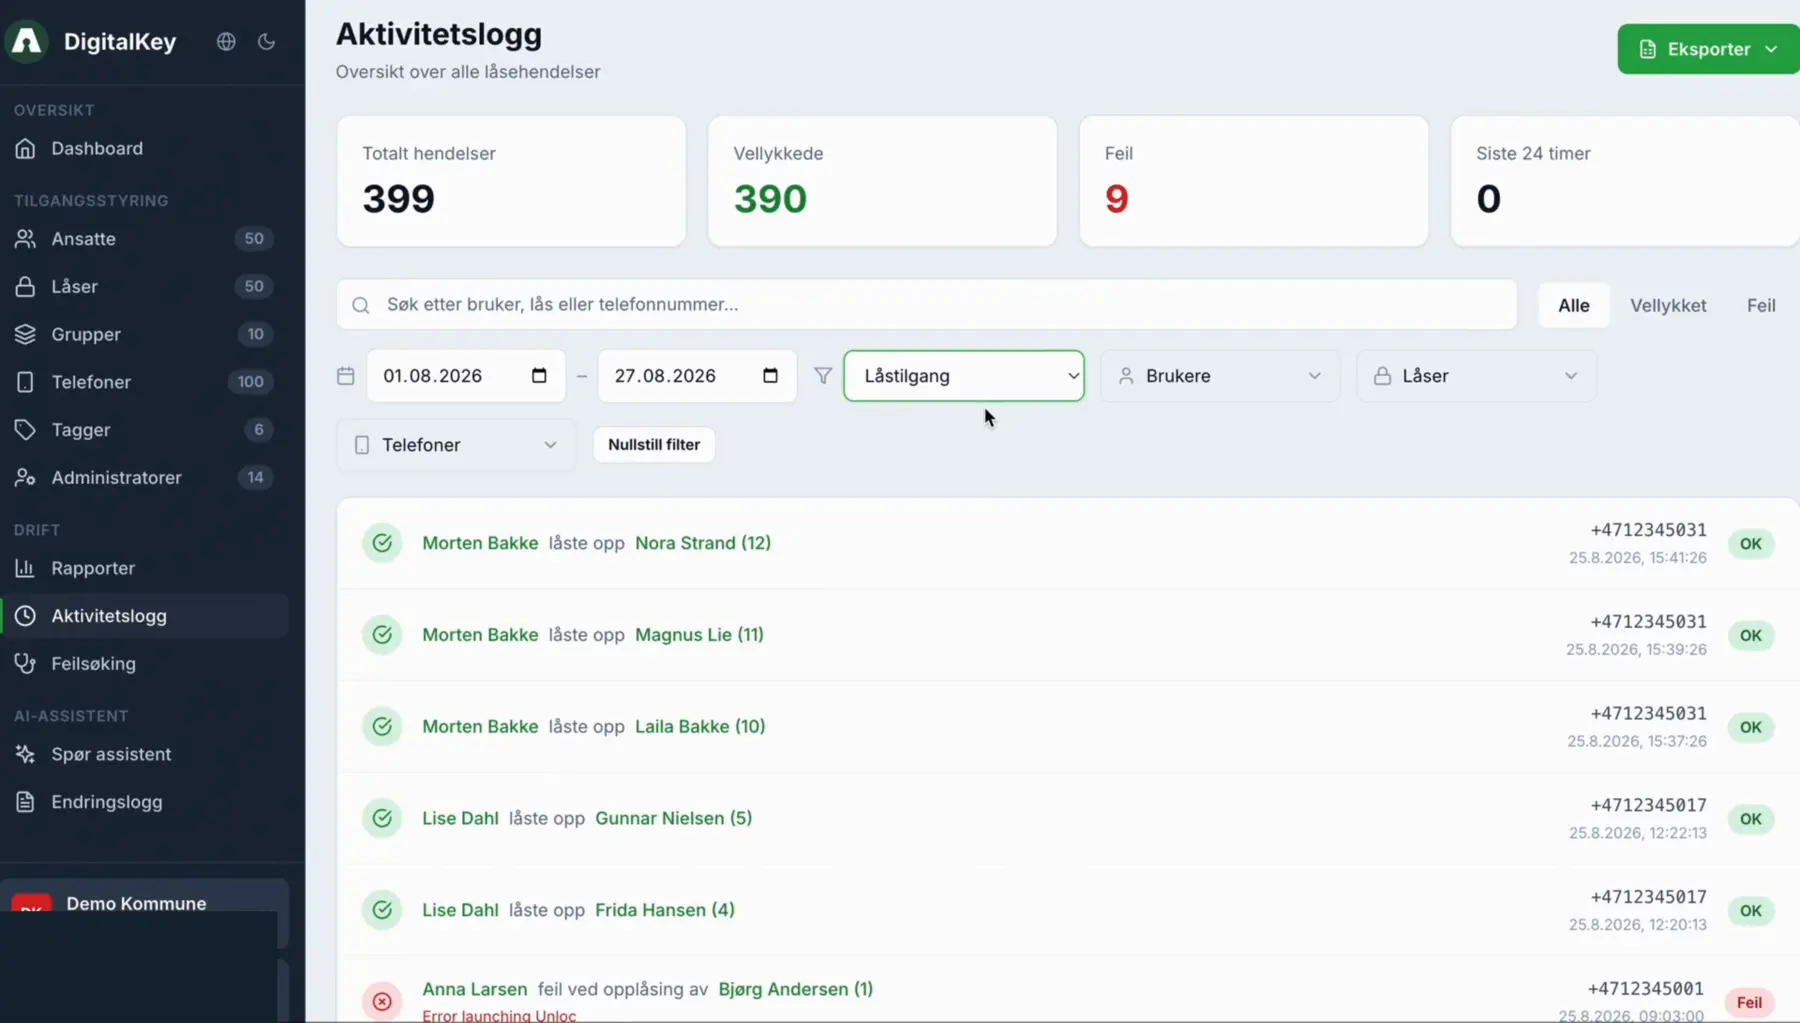
Consider logging user changes, roles, group membership, access assignment and removal, validity periods, lock changes, administrator actions and relevant lock events.
The log should present the time, actor, object and action clearly.
Logging requires follow-up
Define who reviews logs, which incidents are investigated, how events are escalated, how long data is retained and how it is protected.
Secure the administrators
Use strong authentication, personal accounts, least privilege, regular reviews and time-limited elevated access.
Checklist
- Roles are documented
- Every user has an individual identity
- Temporary access expires
- Offboarding is tested
- Administrators are reviewed
- Events are logged and reviewed
- Privacy and retention periods have been assessed
Conclusion
Secure access management is a continuous process. Technology supports the procedures, but the municipality must define responsibilities, legitimate needs and follow-up.
Frequently asked questions
Must every event be retained?
This must be assessed against purpose, risk, technology and regulations.
Can support have full access?
Access should be limited to the need. Read-only or time-limited access is often preferable.
How often should permissions be reviewed?
Use a risk-based approach. Critical roles and external users should be reviewed more frequently.